Testers wanted: ZapperBox tuners as an HDHomeRun source for Channels DVR

I've built an open-source bridge called zapperbridge that makes your ZapperBox tuner appear on your network as a regular HDHomeRun. You add it in Channels DVR like any other HDHomeRun, and the channel lineup and guide data come from your own tuner. It supports multiple ZapperBox tuners merged into one lineup, and it comes as a Docker image (sunnyside1/zapperbridge) with a read-only web page showing tuners, lineup and live streams.

The ZapperBox does all the tuning and decryption itself. The bridge only relays the clean stream the tuner outputs, so it can't play anything the tuner doesn't already output.

Get it: the code and setup guide are at GitHub - jorge123255/zapperbridge: HDHomeRun-compatible bridge for ZapperBox tuners (unofficial) · GitHub, and the image is docker pull sunnyside1/zapperbridge:v0.1.0.

What I'd like testers to try

  • Setting it up from the README, then telling me where it was confusing.
  • Whether it finds your ZapperBox and registers its virtual tuners. This is the part I most need tested, and the log says plainly what happened.
  • Adding it in Channels DVR, checking the channels and guide data, and watching live TV.
  • Two or more channels at once, and recording.
  • If you have more than one ZapperBox, whether they merge into a single lineup.

What helps in a report: your ZapperBox model, how you run it (Docker or native, Linux or Mac), your Channels DVR version, and the container log. For a channel problem, the channel number and time.

Heads up: it's an early release and unofficial. It isn't affiliated with ZapperBox, SiliconDust or Channels. For multiple tuners, the Docker setup works best on a Linux host, since each virtual tuner needs its own address on your network. Docker Desktop on Mac and Windows can't do that part. I've tested it on a Mac against one ZapperBox, but registering fresh tuners from Docker is untested, and so is recording with Channels DVR.

Issues and questions are welcome on GitHub or in this thread.
3 Likes

Glad to see you doing open source again. Who is noreply from China that's responsible for all the commits on GitHub?

lol grok bot it helped me a lot on this

lol right back at you.

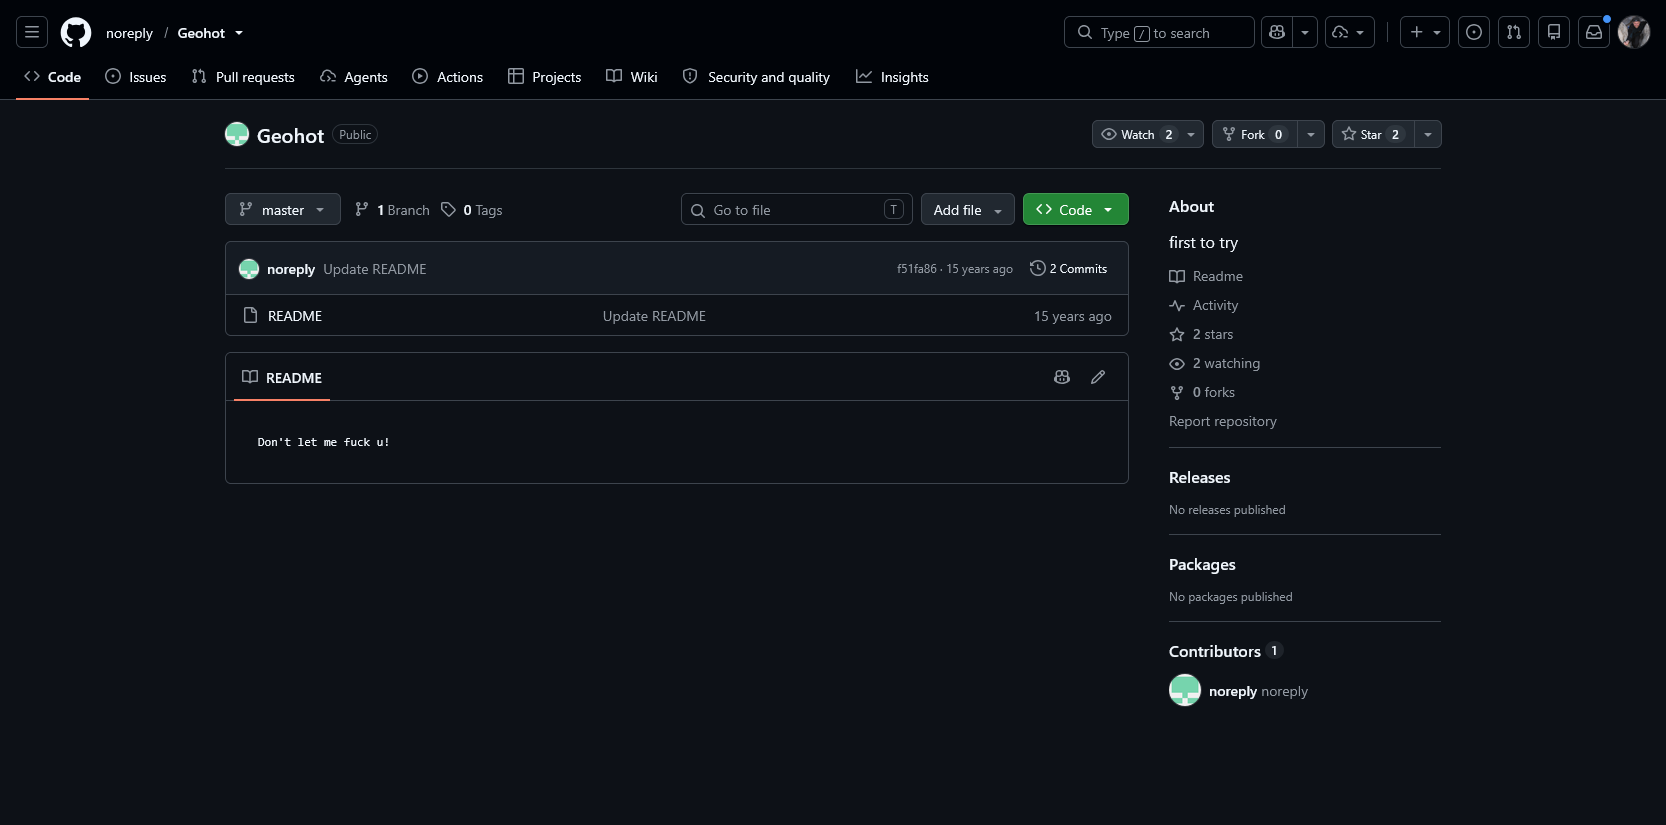
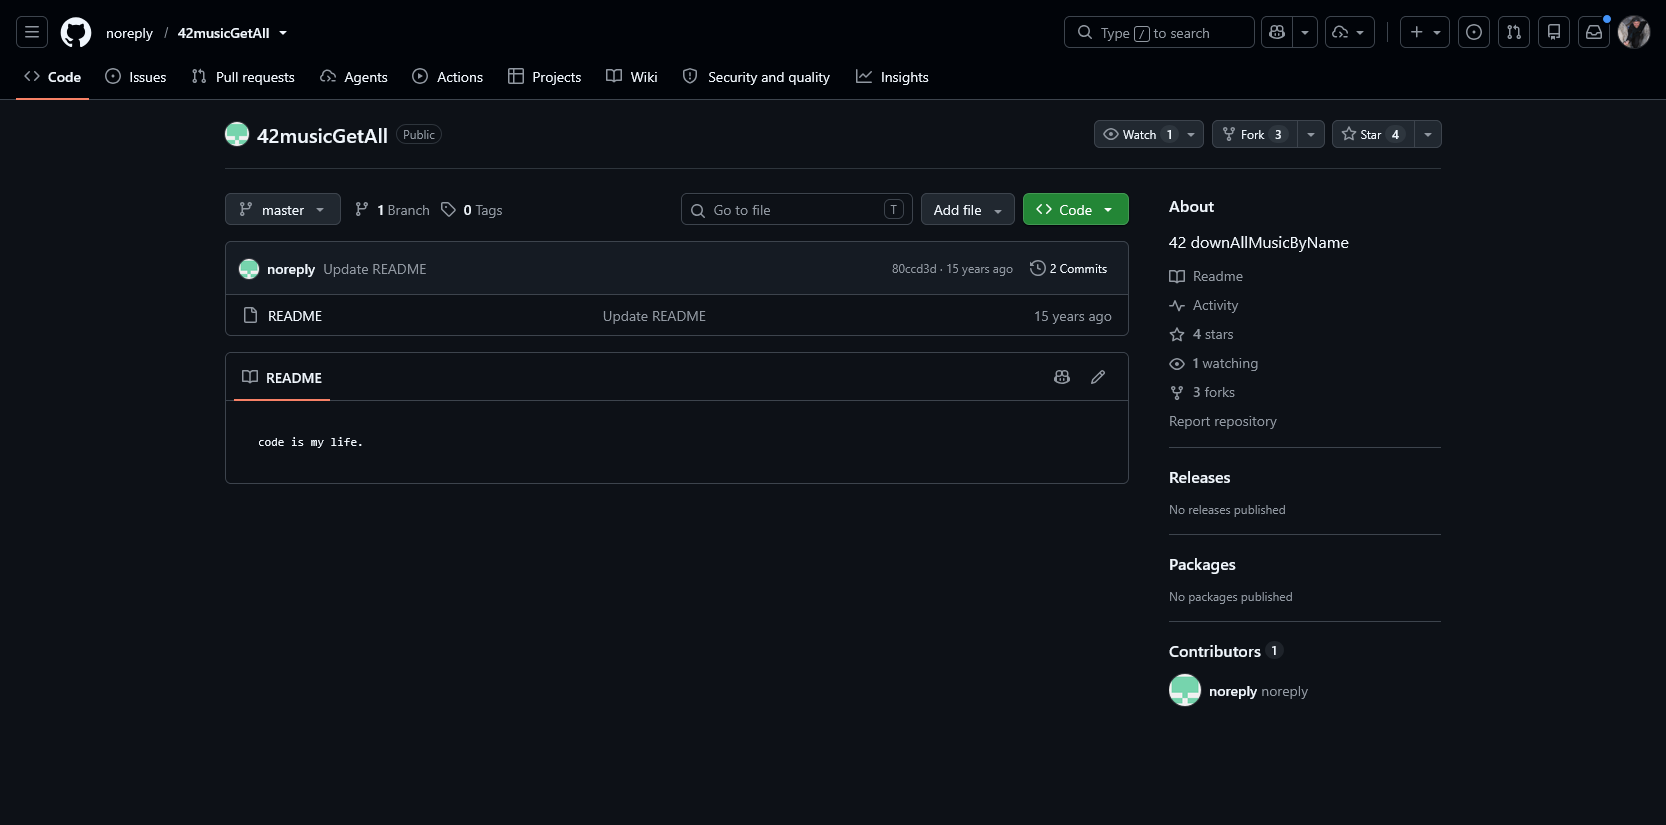
A bit more explanation might be in order. The noreply user that made all the commits, has two other repositories on GitHub. Both have no code, and only the following READMEs:

One of the points of open source software is to be able to both audit the code, and the sources of the code. I'm sure you can appreciate, this raises some questions.

Yeah, that readme is pretty bad.

Cool im checking

Actually, I just had someone open an issue on my Channels DVR Docker container for Unraid users, trying to get me to switch my container to their vibe-coded trash re-implementation of Channels DVR. It was pretty annoying. I just said go away, closed the issue, and locked it. But just the kind of stuff you get on GitHub is ridiculous sometimes.

By the way, as someone who vibe codes a lot of pretty much everything, I have nothing against vibe coding something. I think it's the way of the future. My problem is when you do it badly and blindly trust the model and do zero auditing of what it's done, no cross-checking, no adversarial testing, not writing any tests to confirm that the code is doing what it says it does, that sort of stuff. Always have a sub-agent with clean context do an adversarial audit of your work before you put anything out there, and I would suggest as a technique looping that, and every time it finds something, have it recheck until there are no more issues that it can surface.

The worst thing you can do is write some code, vomit it out into GitHub, and assume it works properly without any bugs, and not do any testing, whether it be physical user testing or automated testing or even just evaluation from a different model or the same model with clean context.

Prompt engineering is extremely important when it comes to agentic coding, and it really comes down to the skill of the person behind the model, not the model.

Bro chill honest mistake.

Also I tested all this before releasing 1 week of testing.

What the heck? I was just kind of giving you some pointers as someone who writes a lot of code. And saying, don't look here ** you is not an honest mistake; it's the sign of someone who doesn't know what the heck they're doing and leads to anyone looking to actually try their project. I was trying to give you a little bit of advice to maybe drive your model a little bit better, but if you want to talk to me that way, I think maybe, hopefully, no one tests your code if this is how you treat others.

Like, my comment wasn't meant to be harmful to you; it was meant to give you genuine advice as to better catch issues before releasing to the public.

1 Like

Cool thanks

What is your problem? I'm trying to help you. I think this is a cool idea, and I was just trying to give you some advice as someone who's written probably a few hundred thousand lines of code with Claude. Like, genuinely trying to help.

No harm intended. I don't understand the passive aggression, but I am going to, you know, have to ping the moderation team here to maybe look into this and see if this is something even safe to put in the community, given the way you're treating others here. It's not acceptable. @bnhf do you mind stepping in here? I meant no harm to this user and was just trying to help them improve their project and processes based on my knowledge. Given their README actually contained profanity, I thought maybe I could lend some advice to help them drive their model.

No passive lol all I said cool thanks

You know, cool thanks can be read either way.

Based on prior context of the conversation, it was read to me as being semi-passive-aggressive, and if it wasn't, then that's just how things are sometimes read over text, and I'm glad it wasn't.

No problem all good :slight_smile: welcome to make changes and fixes as u like to the code

1 Like

Didn’t make this one private as I thought channels could use a alternative to HDHomeRun with ASTC3 took lots of hard work get this over the line but again it’s def beta I used it and played well in channels :slight_smile:

I agree it's a very cool idea, and I hope we can move forward with it. @gszulc, there aren't that many of us that really drill down to look a code, and its sources, in these community projects. But those of us that do, will give you honest feedback about what looks right, and what doesn't.

I couldn't find any corroboration that grok uses noreply from China as a GitHub user. If you can correct what we're seeing, and we can run a code audit, we'll all be safer (including you).

2 Likes

I agree 100%. All I want to do is help and maybe provide some prompt engineering advice!

1 Like

Love it idk we’re grok bot went off the rails lol there just asked it to publish it for me and put that in the comments lol but this is his reply im honest will tell u there members in here using other projects of mine that will tell u I mean no harm

That's my mistake, and it has a harmless explanation. I set the commit author to zapperbridge [email protected] so your real name and email wouldn't appear in the public history. But that exact address belongs to a real GitHub account named "noreply", and GitHub links any commit using it to that account. So the commits show up under a stranger's profile, and I understand why the person who noticed asked questions. No code came from that account. All the code is ours, and I didn't mean to impersonate anyone.

The clean fix is to use your own GitHub private address ([email protected]) for the commits. For the 14 existing commits there are two ways to fix it:

  • Rewrite the history with the correct author, then force-push main and re-point the v0.1.0 tag. It cleans the history, but it replaces the public commits. Anyone who already cloned the repo would need to re-clone, and the release notes stay valid.
  • Leave the history, set the right address for all new commits, and post a short note on the repo explaining the old ones.

I'd rewrite it now, since the repo has only been public for about an hour. The Docker Hub image doesn't depend on the commit authors, so it isn't affected. A force-push changes public history, so I need your OK first.

Dam grok

1 Like